



What is GRC? Your need-to-knows
GRC is a structured approach to aligning an organisation’s governance, risk management and compliance activities, so that objectives are achieved reliably and with integrity. In this blog, we’ll answer four questions:
- What does GRC stand for?
- Why is GRC important?
- What is the GRC capability model?
- What is GRC software and why do you need it?
What does GRC stand for?
GRC stands for Governance, Risk Management and Compliance. Rather than treating the three as separate disciplines, GRC brings them together into one joined-up approach.
Why is GRC important?
Benefits of effective GRC include:
- More agile decision-making
- A more collective approach
- Improved senior managers’ confidence
- Better ROI on IT purchases
- Less working in silos
- Time and money saved by removing activities that don’t add value
- No duplication of activities
- Information gathered quickly and efficiently
- More detailed and productive reporting
- Teams able to repeat processes more consistently
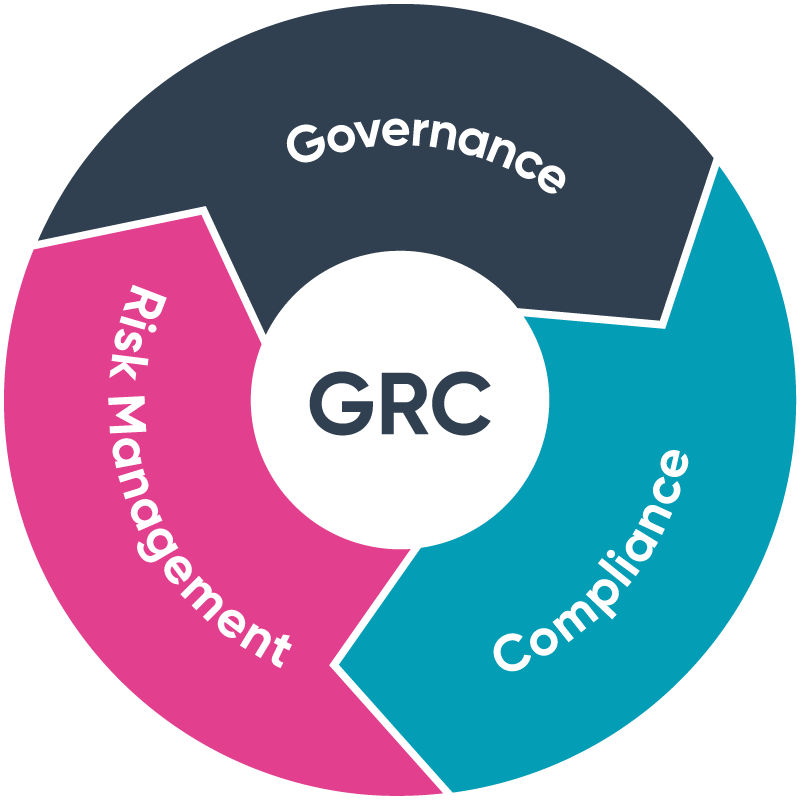
GRC is an acronym for Governance, Risk Management and Compliance, but the OCEG (a nonprofit think tank) states that the full story is much more than those three words.
The acronym, first introduced in 2003, refers to the capabilities that combine to achieve what’s known as ‘Principled Performance’: the ‘reliable achievement of objectives while addressing uncertainty and acting with integrity.’ In other words, a successful organisation is consistently competent at evaluating risk, managing uncertainty and adapting to changing circumstances.
But haven’t organisations always had to manage risks and unknowns? If so, why do we need an acronym like GRC? Well, a GRC framework is a mature and systematic approach to governance, risk and compliance. It is employed for high-level decision making at the top of an organisational structure.
According to the OCEG, a strong GRC approach enables:
- the right people to get the right information at the right times
- the right objectives to be established
- the right actions and controls to be put in place to address uncertainty
Before we move on to look at the GRC Capability Model (the OCEG’s core standard), let’s look at the three areas of governance, risk and compliance in a little more depth.
Governance
What is governance? In simple terms, governance is about authority, decisions and accountability for results. The term refers to the actions an organisation takes to ensure that activities are aligned to support business goals and values. It is a system of rules, policies and processes that include ethics, resource management, accountability and management controls.
Strong governance:
- empowers people at all levels of the organisation to work together to achieve common goals
- ensures that customers’ needs are prioritised and aligned to business units
- provides management of facilities and infrastructure
According to IBM, ‘effective governance creates an environment where employees feel empowered and behaviors and resources are controlled and well-coordinated.’
Risk
Risk management is about acting proactively instead of reactively. It is the actions an organisation takes to control, as best as possible, future results and outcomes. Effective risk management aims to reduce the possibility of a risk emerging and mitigate its potential impact on the organisation and its productivity.
Three verbs that we associate with risk management are:
- identify
- assess
- control
Risk management does not only apply to risk and compliance professionals. It is embedded throughout an organisation via processes and technologies designed to help mitigate risk.
The different areas of risk are:
- financial
- legal
- strategic
- security (including cybersecurity and information security)
To manage risk, an organisation must be able to stay ahead of the game by identifying risks, assessing their potential impact and applying resources to monitor them.
Compliance
Put simply, compliance means adhering to rules. In the world of business, these might be standards, laws and policies implemented by industry regulators, independent organisations or governments. For example, many businesses choose to comply with ISO 9001:2015, an international standard for quality management systems. When companies do not comply with mandatory rules and regulations, they risk costly fines, penalties, lawsuits and damage to their reputations.
There are different areas of compliance within an organisation:
- Corporate or internal compliance deals with any rules and controls that have been set by the company itself.
- Regulatory compliance works to ensure the company complies with external laws, regulations and industry standards. A regulatory compliance solution helps you keep track of these requirements in one place.
In fact, some people think that the ‘C’ in GRC refers to control, a word which is often equated with the term compliance.
What is the GRC capability model?
The GRC capability model 3.0 is an open-source standard created by the OCEG. It is commonly known as the ‘Red Book’.
It was designed to integrate ‘the various sub-disciplines of governance, risk, audit, compliance, ethics/culture and IT into a unified approach.’
The OCEG studied 250+ organisations to identify best practices in GRC. They found that the four components of the GRC capability model 3.0 are:
- LEARN. When it comes to GRC, knowledge is power. This is about developing an enhanced understanding of an organisation and the specific context in which it operates. It’s about absorbing a company’s culture and getting to know the main stakeholders in order to set appropriate goals and create informed strategies.
- ALIGN. This is about ensuring that all the different parts of the organisational ‘machine’ are connected and flowing seamlessly together. Strategies should be aligned with objectives and actions with strategies. Decision-making should address opportunities, corporate values, risks and requirements.
- PERFORM. This relates to the performance of actions. All actions should be intentional rather than perfunctory. Good governance should promote and reward desirable actions, while preventing and remediating undesirable ones.
- REVIEW. Measures should be taken to assess the design and operating efficiency of the strategy and actions. With a growth mindset, the organisation should consistently look for opportunities to review the appropriateness of objectives and find ways to improve them.
What is GRC software?
GRC software is a digital platform that enables a company to manage its operations and compliance activities in one place. It is sometimes also called a GRC tool, GRC solution or GRC system. It should enable users to manage operational risk, internal audit, IT governance, and policy and compliance.
Why do you need GRC software?
Contemporary technology can work wonders for GRC by automating processes and providing valuable management reports. Here are some of the key benefits of a GRC solution:
- Eliminates manual processes that breed risks and mistakes
- Real-time collaboration on projects
- Makes administrative processes easy and frictionless
- Centralised document management
- A bird’s-eye view of GRC-related workflows
- Advanced and streamlined reporting for auditors
- Provides full audit trails
- Improves senior managers’ confidence
- Safeguards against fines and sanctions
- Robust, multi-level security to protect against sensitive data breaches
- Empowers employees to work remotely without risks to privacy and security
With an effective GRC tool, your company can elevate its GRC processes to ensure compliance with important industry-specific standards and regulations. To see how this works in practice, explore Ideagen’s regulatory compliance solution. While a software investment might come with a price tag, it will streamline processes and save you both time and money in the long term.
Ultimately, however, a strong GRC culture cannot simply be purchased. While software can dramatically improve GRC in any business, it must work in tandem with people. As Joseph Mathenge argues, ‘Technology doesn’t have ethics—people do.’ This is why leaders must address GRC from a holistic perspective, considering people, processes and technology, and take steps to encourage employees’ buy-in to GRC practices at every level of the organisation.
Explore policy management solutions
Solutions to streamlines governance with a tailored offering for compliance and risk management, ensuring organizations meet regulations efficiently and effectively.