Now that we’ve looked at different areas to consider when assessing your ISO 31000 risk management framework, let’s focus on how to carry out a risk assessment in the eighth instalment of our ISO 31000 blog series.
What is a risk assessment?
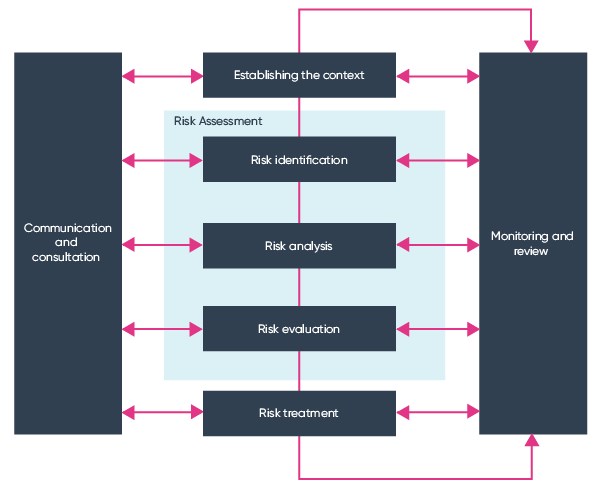
A risk assessment is the process of identifying the risks your organisation faces, understanding how likely they are and how serious their consequences would be, and deciding which ones need action. In ISO 31000, risk assessment is made up of three steps: risk identification, risk analysis and risk evaluation. The results feed directly into your decisions on risk treatment.
Once the context of the organisation and the scope of the risk management strategy are defined, the risk criteria can be identified and developed (Clause 6.3). These criteria establish the way risks are recognised and recorded, and they shape how you carry out an ISO 31000 risk assessment.
The next step of the ISO 31000 framework is Clause 6.4, the overall process of risk identification, risk analysis and risk evaluation. The whole process is designed to be systematic, iterative and collaborative, so that a comprehensive and integrated risk management strategy is developed. At every stage of the risk assessment, communicate with and involve key internal and external stakeholders where required, so you can draw on broad experience and knowledge to build a strong strategy. Risk management software can help you record, score and track the results in one place.
Clause 6.4.2: Risk identification
The first step in an ISO 31000 risk assessment is risk identification. You are required to find, understand and describe risks. Remember that a risk is something that could hinder, prevent or even help an organisation to achieve its strategic objectives.
During risk identification, use the latest information available. Factual, timely and accurate data will enable you to develop the most relevant strategy. Factors to consider when identifying a potential risk to your organisation may include:
- Tangible and intangible sources
- Causes and events
- Threats and opportunities (even positive risks need to be assessed)
- Existing capabilities for handling risk, and any vulnerabilities
- Contextual changes, such as a change to an external factor
- Resources available, and their nature and value
- The likelihood and consequences of a risk
- The severity of a risk should it occur
- Knowledge gaps (the known unknowns)
- Time and resources allocated to the risk management team
- The bias, experiences and assumptions of the stakeholders involved in the risk assessment
When identifying a risk, note that there may be more than one outcome if it occurs, and that this may affect other risks you have identified.
Clause 6.4.3: Risk analysis
Risk analysis allows decisions to be made about risk treatment and helps define the organisation’s risk appetite. The type, level and likelihood of a risk are all taken into consideration, alongside detailed factors such as available resources and internal and external influences.
One risk incident can have multiple possible outcomes, and these may affect further risks. Consider the domino effect of a risk within the context of the organisation’s objectives.
There are many techniques for analysing risk, and it is up to the organisation to define which ones it uses. Some of this is covered in Clause 6.3, as the context of the risk strategy includes the definition of risk criteria and
Clause 6.4.4: Risk evaluation
The final stage in the risk assessment process is risk evaluation. Evaluation allows an organisation to make decisions about risk treatment and prioritise risk mitigation with ease.
Risk evaluation compares the results of the risk analysis against the risk criteria to determine:
- How effective the criteria definition is
- Which risks are the highest priority
- How to approach the next steps (risk treatment)
- How successful the risk analysis process was (are there any knowledge gaps remaining?)
The outcome of a risk evaluation could lead to several actions: you may need to assign further analysis, maintain your existing controls, or reconsider the objectives of the risk strategy so they align with the organisation’s objectives.
Regular evaluation allows you to develop a comprehensive and mature risk management strategy, as changes to risk factors, impact, consequences and objectives can be addressed in a reasonable time frame. Ideagen Risk Management helps you keep each assessment, score and review date in one place.
Now that you know how to carry out a risk assessment, find out how one of our customers improved their CAPA risk assessment process with our software.
Explore risk management solutions
Roll up your risk into one system for full visibility, maximum control coverage and joined-up reporting.